Terraform Basics
To set up an EC2 instance in AWS using basic commands like terraform init, terraform plan, terraform fmt, terraform apply, and terraform validate.
Imagine you’re playing with LEGO blocks and want to build a big LEGO city with houses, roads, and parks. But instead of putting the pieces together by hand every time, you can write down instructions so that a robot can build it for you.
Terraform works similarly to that robot.
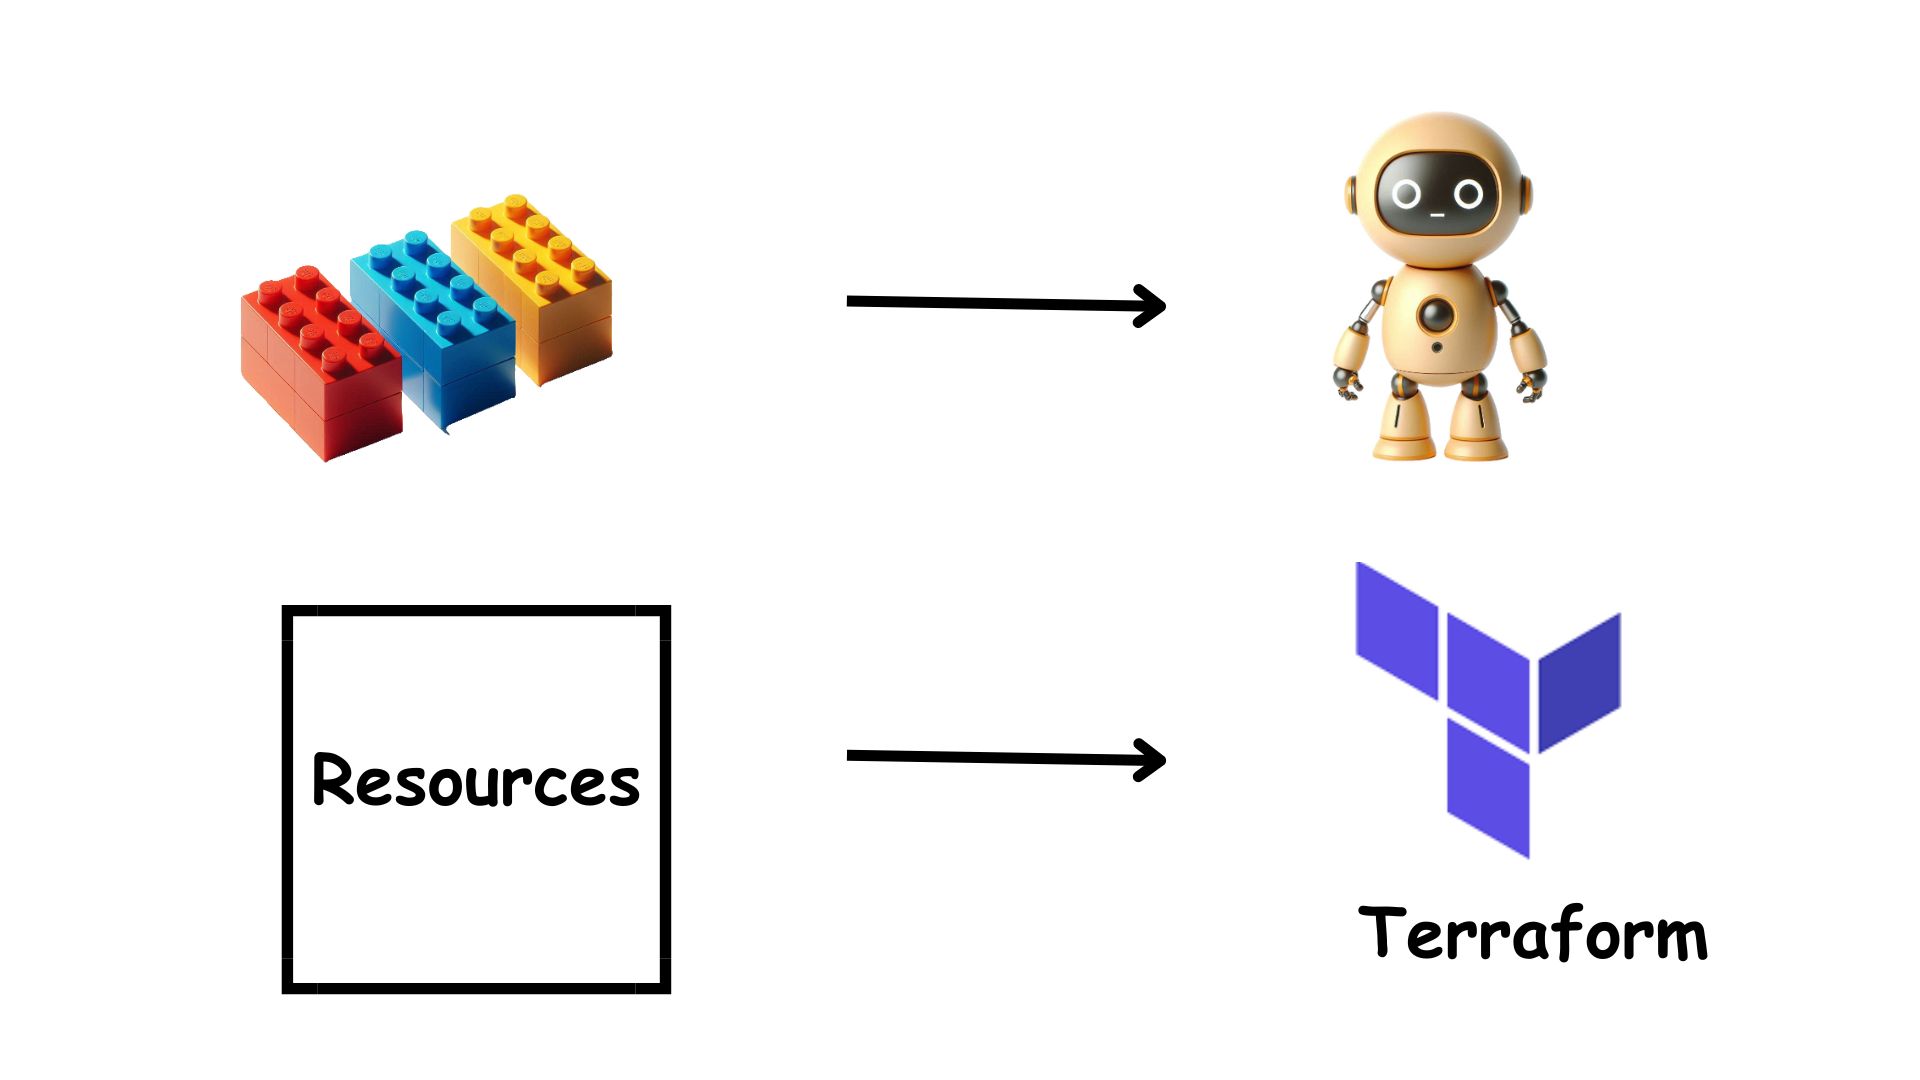
It's an open-source tool to define and manage the Infrastructure-as-Code (IaC).
You'll be writing the configuration file, and Terraform will apply the instructions provided. These instructions will specify the features of the resources and other relevant details.
Instead of manually setting up servers, databases, networks and other resources you write code to define what you want. This code is written in HashiCorp Configuration Language (HCL).
It works with many cloud providers (like AWS, Google Cloud, Azure) and on-premises data centers.
Images from Terraform documentation
How Terraform works:
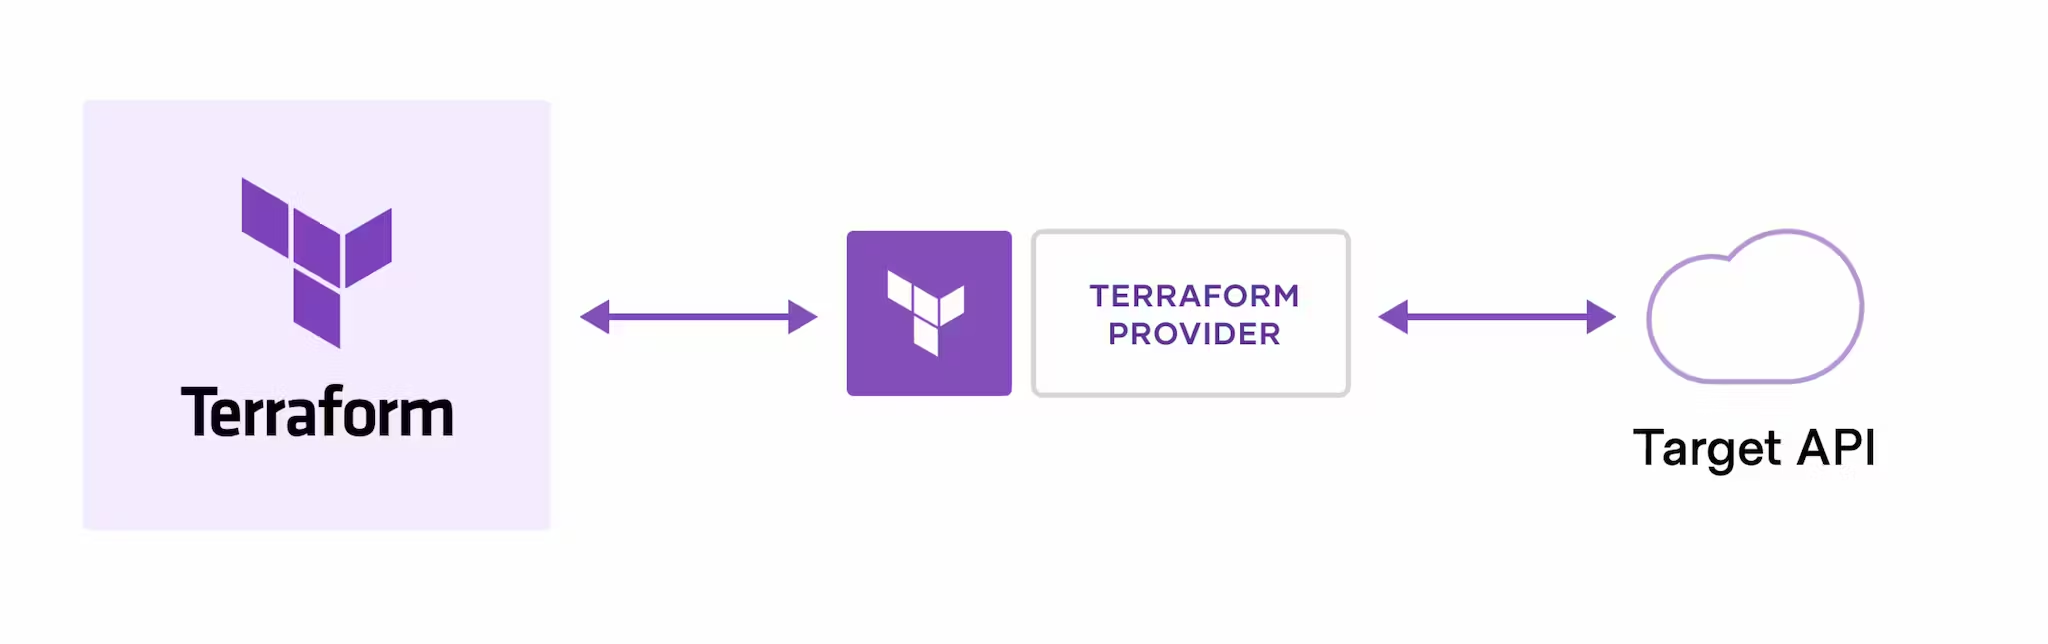
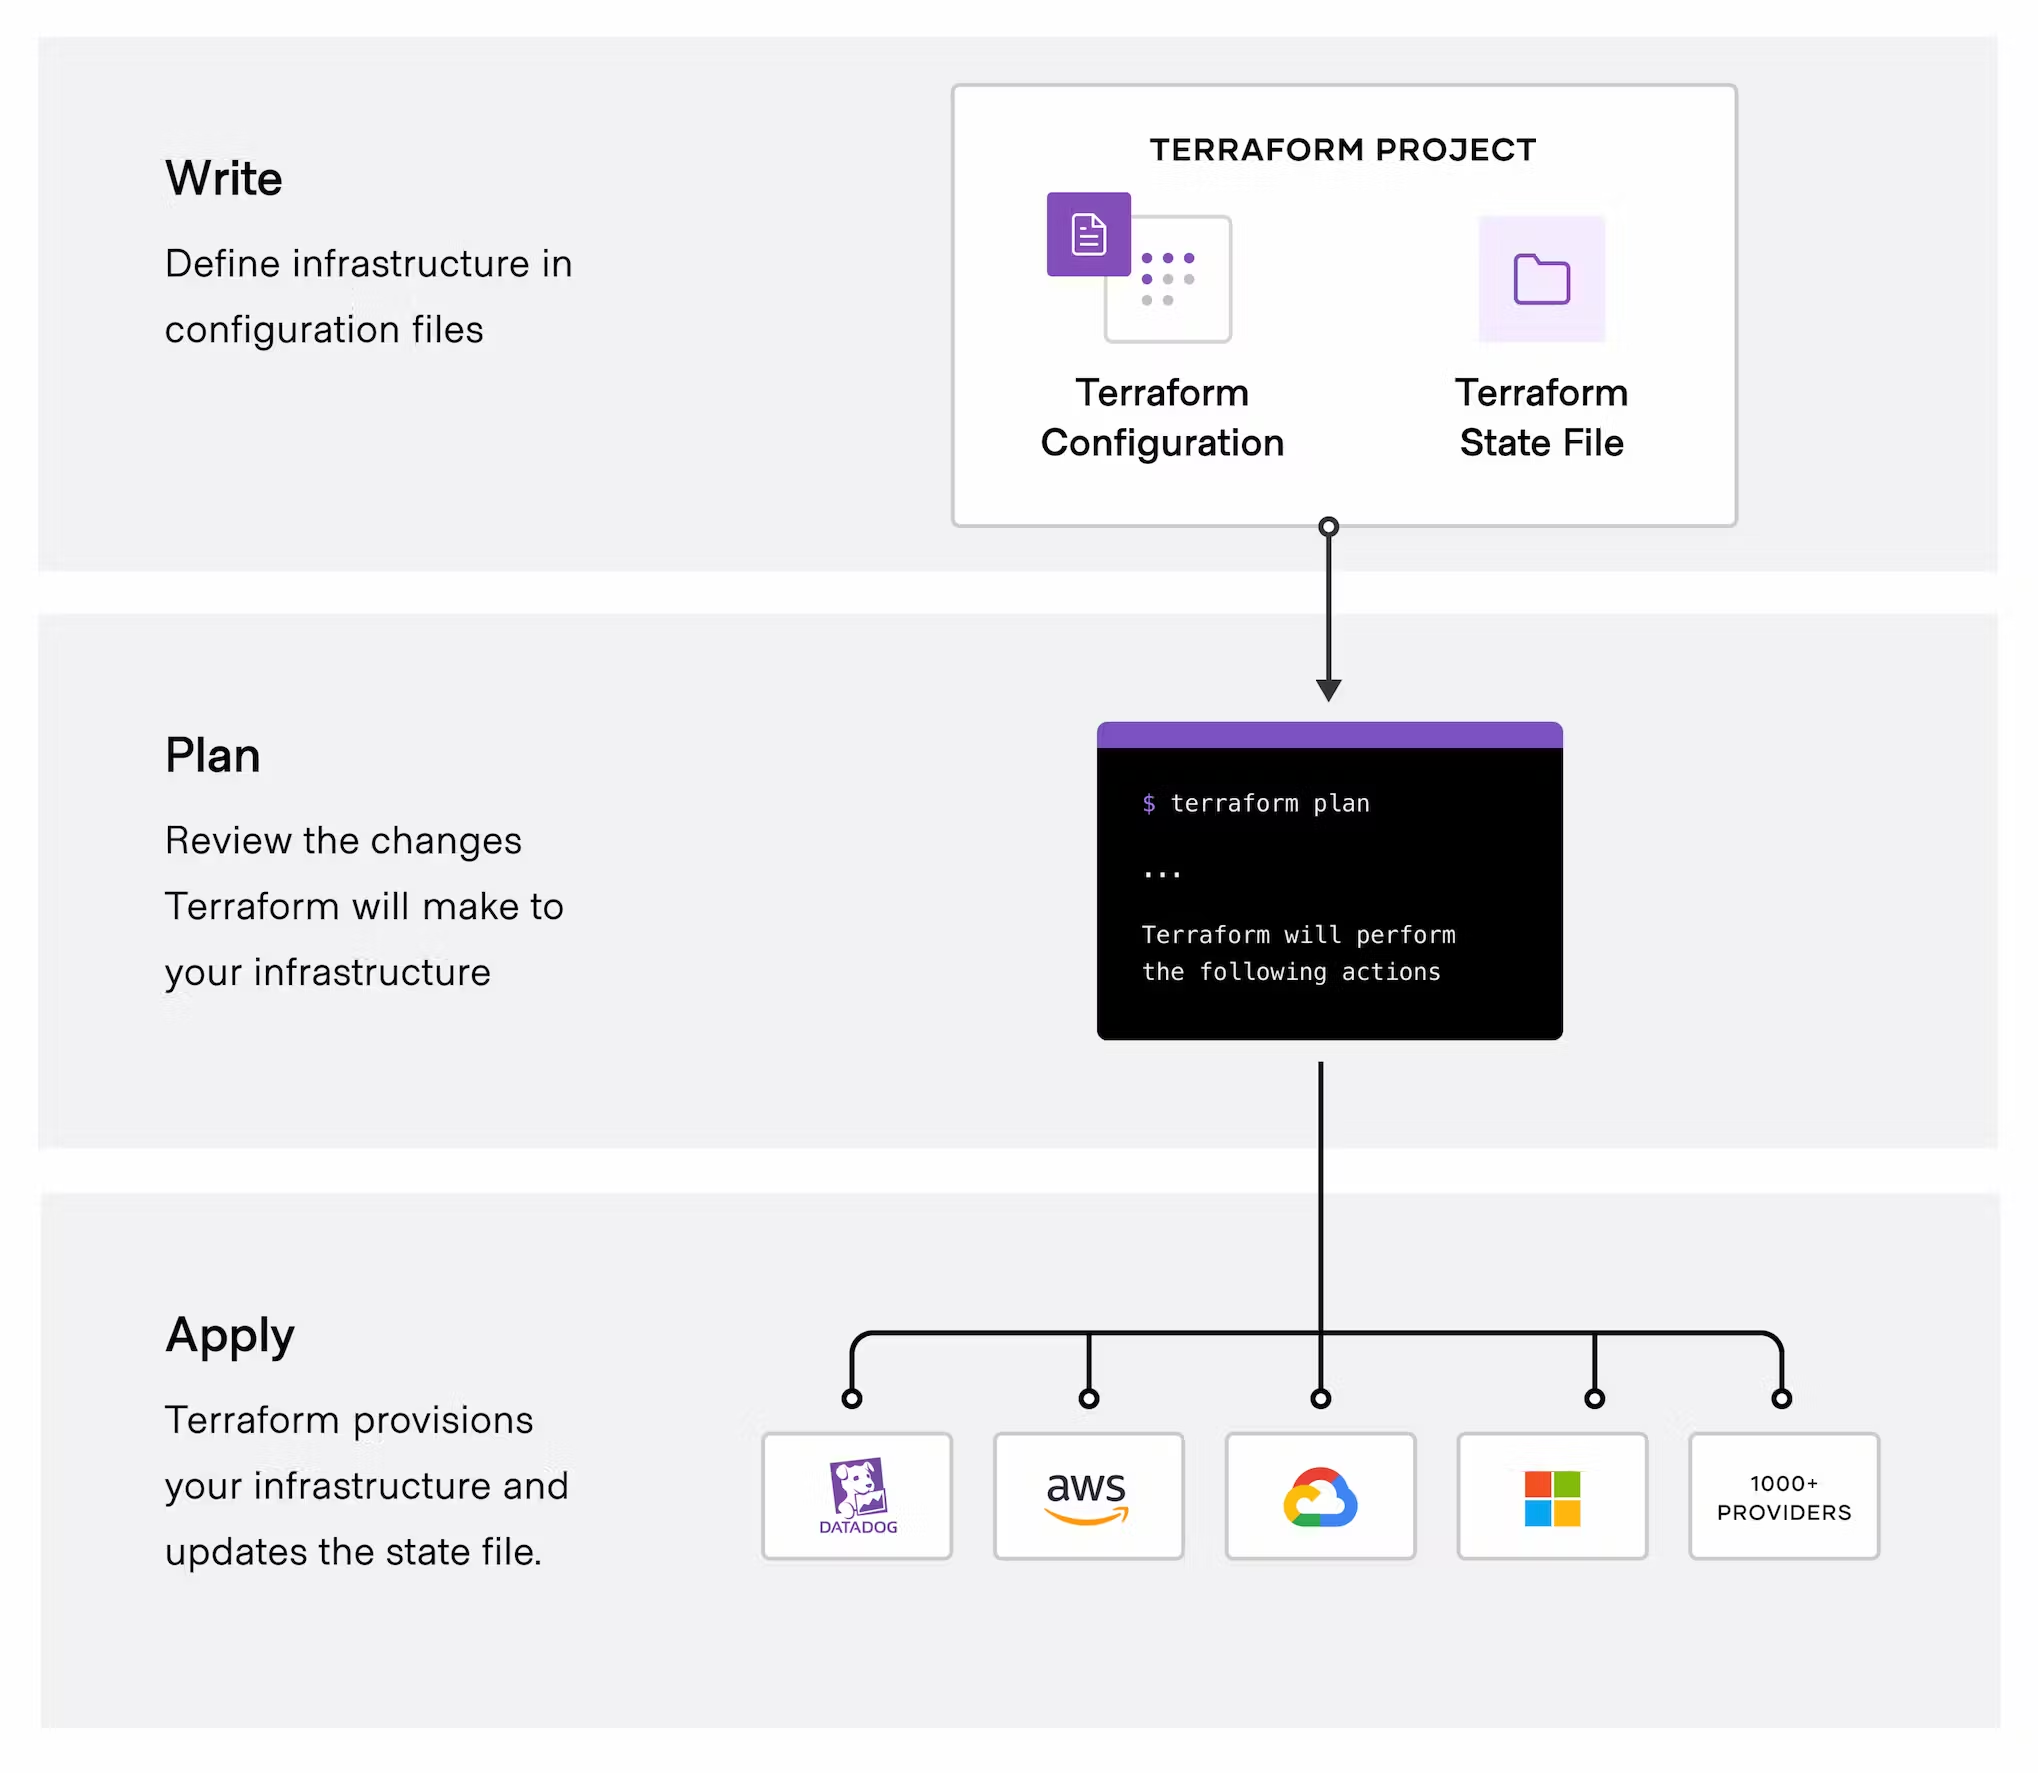
Open Gitbash or any other similar tool.
aws configureThis command initiates the AWS CLI configuration process. When you run aws configure, you will be prompted to enter your AWS Access Key ID, Secret Access Key, default region name, and default output format. This sets up your AWS CLI environment to interact with AWS services.
aws configure
cd /dThis command changes the current directory to the root directory of the D: drive in Windows operating systems. Thecdcommand stands for "change directory" and it is used to navigate between directories in the command line.
cd /d
mkdir terraform-examplesThis command creates a new directory namedterraform-examplesin your current working directory. Themkdircommand stands for "make directory" and it's used to create new directories in Unix-like operating systems.
mkdir terraform-examples
mkdir exercise1This command creates a new directory namedexercise1in your current working directory(terraform-examples).
mkdir exercise1/
cd exercise1/This command changes the current directory to theexercise1directory within your current working directory.
cd exercise1/
vim first_instance.tfThis command opens the filefirst_instance.tfin the Vim text editor. If the file does not exist, Vim will create a new file with that name.
vim first_instance.tf
- Inside the terraform file determine this configuration (https://github.com/Ragavi04P/Terraform-Practice/blob/main/first_instance.tf)or similar configuration for which resource you should use.
This Terraform configuration defines an AWS provider and an AWS EC2 instance resource. Here's a brief explanation of each part:
- This block specifies the AWS provider and sets the region to
us-east-2.
provider "aws" {
  region = "us-east-2"
}
resource "aws_instance" "intro" {
  ami                    = "ami-03657b56516ab7912"
  instance_type          = "t2.micro"
  availability_zone      = "us-east-2a"
  key_name               = "your key pair name"
  vpc_security_group_ids = ["your sg id"]
  tags = {
    Name    = "sample-Instance"
    Project = "Terraform"
  }
}
This block defines an AWS EC2 instance resource named
intro.amispecifies the Amazon Machine Image ID to use for the instance.instance_typesets the type of instance tot2.micro.availability_zonespecifies the availability zone within the region.key_nameis the name of the key pair to use for SSH access.vpc_security_group_idsis a list of security group IDs to associate with the instance.tagsassigns metadata to the instance, such asNameandProject.
terraform initThis command initializes a Terraform working directory. It prepares the directory by downloading and installing the necessary provider plugins and setting up the backend configuration. This is the first command that should be run after writing a new Terraform configuration or cloning an existing one from version control.
terraform init
terraform fmtThis command formats the Terraform configuration files in the current directory to a canonical format and style. It ensures that the code is properly indented and organized, making it easier to read and maintain.terraform fmtterraform validateThis command checks the syntax and validity of the Terraform configuration files in the current directory. It ensures that the configuration is syntactically correct and that all required arguments are specified. This is a useful step to catch errors before applying the configuration.
terraform validate
terraform planThis command creates an execution plan, showing what actions Terraform will take to achieve the desired state defined in the configuration files. It compares the current state with the desired state and lists the changes that will be made such as creating, updating, or deleting resources. This allows you to review the proposed changes before applying them.
terraform plan
terraform applyThis command applies the changes required to reach the desired state of the configuration as defined by the Terraform files. It creates, updates, or deletes infrastructure resources to match the configuration. Before making any changes, Terraform will show a plan of the actions it will take and ask for your confirmation.
terraform apply
This command lists the files and directories in the current working directory.
ls
cat terraform.tfstateThis command displays the contents of theterraform.tfstatefile in the terminal. Thecatcommand is used to concatenate and display the content of files in Unix-like operating systems. Theterraform.tfstatefile contains the current state of your infrastructure as managed by Terraform.
cat terraform.tfstate
A state file in Terraform records the current state of your infrastructure, mapping your configuration to real-world resources. It helps Terraform determine what changes need to be applied to reach the desired state. The state file is essential for tracking and managing infrastructure efficiently. The output will be in JSON format.
cat terraform.tfstate.backupThis command displays the contents of theterraform.tfstate.backupfile in the terminal. Theterraform.tfstate.backupfile is a backup of the state file, which contains the previous state of your infrastructure as managed by Terraform.
cat terraform.tfstate.backup
terraform destroyThis command is used to destroy the infrastructure managed by Terraform. It will remove all the resources defined in your Terraform configuration files. Before making any changes, Terraform will show a plan of the actions it will take and ask for your confirmation. This is useful for tearing down environments or cleaning up resources that are no longer needed.
terraform destroy
These are the terraform basics that you need to know for setting up the infrastructure for a cloud environment.